JORDAN MEISELS / SECURITY ENGINEERING

Security engineering, grounded in investigation.

Security engineering, grounded in investigation.

Security engineering, grounded in investigation.

I specialize in incident response, threat hunting, and detection engineering, combining investigative experience with security automation, Python development, and applied AI experimentation to build actionable detections and practical security tools.

I focus on threat hunting, incident response, detection engineering, and practical security automation, turning investigative questions into clear evidence and useful tooling.

KQL · Python · PowerShell · Docker · Microsoft Sentinel · Microsoft Defender · REST APIs

FEATURED PROJECTS

FEATURED PROJECTS

Sample-data prototype

Password Spray Analyzer

Password Spray Analyzer

Password Spray Analyzer

Python · Docker / Containerization · Entra ID · REST APIs

A Python prototype for identifying potential password spraying in sample Entra-style sign-ins, with AI summaries and local or Docker execution.

Sample sign-ins → Python detection → AI summary.

Sample data. No live Entra ingestion.

View repository ↗

Threat-informed hunt

Threat-informed hunt

Twill Typhoon Hunt

Twill Typhoon Hunt

KQL · Microsoft Defender · Threat Hunting

KQL · Microsoft Defender · Threat Hunting

KQL correlating executable extraction, file relocation, and scheduled task creation to identify investigation candidates informed by Twill Typhoon intelligence.

Extracted files → Hash correlation → Scheduled task review.

Hunt code is public. The source intelligence report remains confidential.

TECHNICAL WORK

Practical work. Inspectable methods.

Practical work. Inspectable methods.

Practical work. Inspectable methods.

CURRENTLY BUILDING

In development

Incident Enrichment Platform

A separate platform initiative for gathering and structuring incident evidence.

Current work: Microsoft Graph-based evidence retrieval and parsing.

Planned: enrichment routing · AI summaries · business-context integrations · downstream workflows

In development

Incident Enrichment Platform

A separate platform initiative for gathering and structuring incident evidence.

Current work: Microsoft Graph-based evidence retrieval and parsing.

Planned: enrichment routing · AI summaries · business-context integrations · downstream workflows

About Me

About Me

About Me

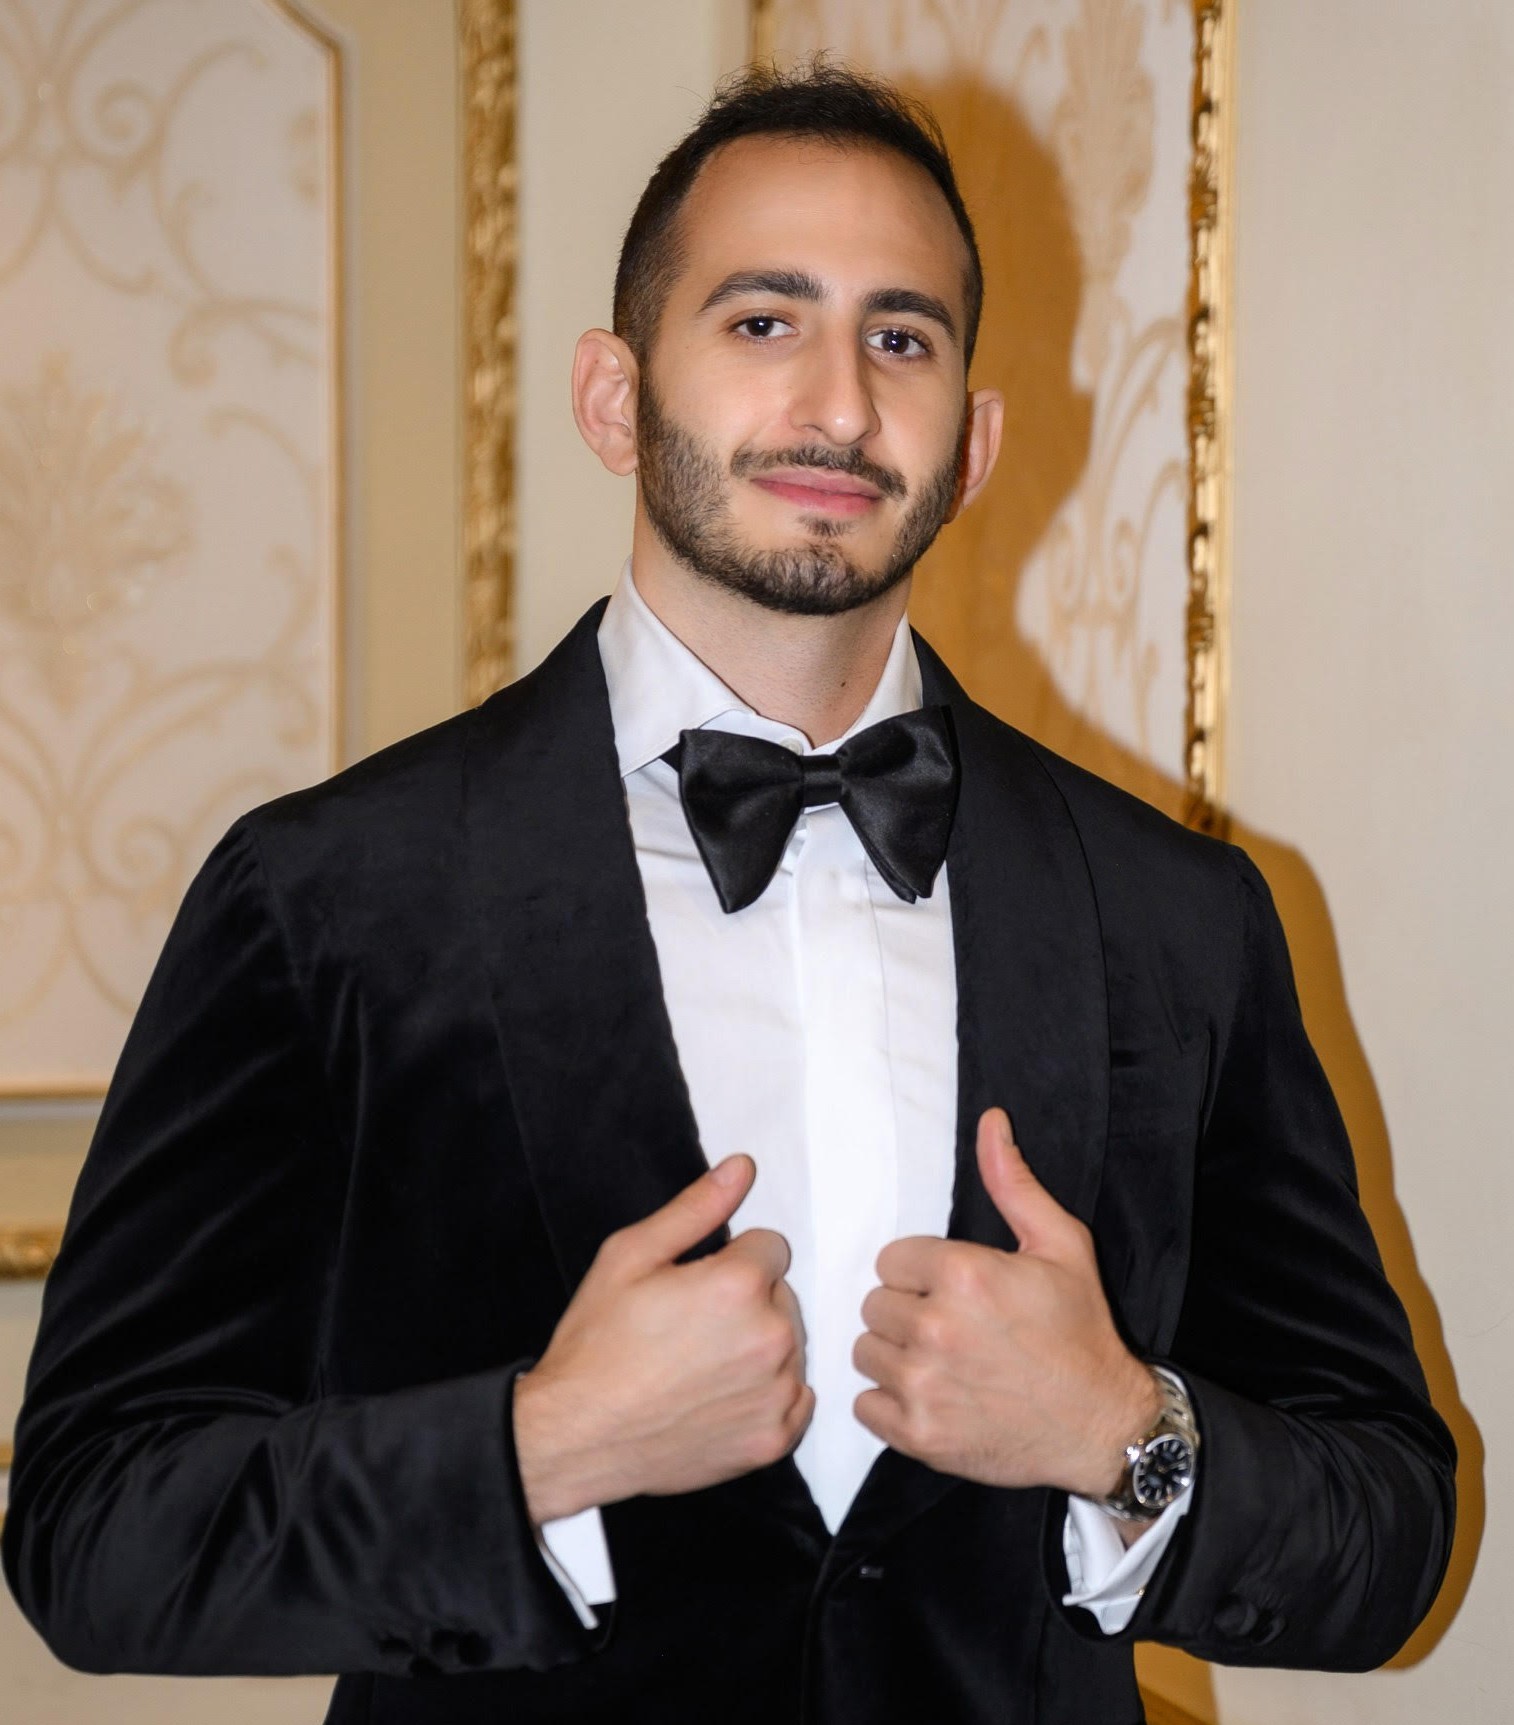
Jordan Meisels.

I’m Jordan Meisels, a Canadian military veteran and cybersecurity professional based in Brooklyn, New York, and Salt Lake City, Utah.

At Rio Tinto, my experience spans vulnerability management, incident response, threat hunting, and purple team operations, including an interim management role.

I build practical detections and automation with Python, PowerShell, KQL, and APIs. My approach is investigative: follow the evidence, understand the behavior, and turn findings into useful improvements.

Outside of work: cycling, fitness, gaming, travel, and cooking.

Download My Resume

TECHNICAL SKILLS

Demonstrated: Python · PowerShell · KQL · Docker · REST APIs · VirusTotal · Microsoft Defender

Applied in projects: authentication-log analysis, containerization, API integration, and investigation summaries.

CONTACT

Open to all conversations.

Open to all conversations.

Open to all conversations.

Interested in security engineering, detection and response, threat hunting, and security automation opportunities.

New York City / Salt Lake City

Jordan Meisels | Security Research & Engineering